

Product
paytech Achieves PCI DSS Level 1: Elevating Payment Security and Trust
 White Label Payment Gateway
Unlock your global payment business potential. Discover the power of our white label solution, enabling you to swiftly launch your own cutting-edge payments platform.
Payment Orchestration
Manage payment processing in a streamlined and efficient manner.
Latest success story

Roman Andriichuk
Director, Exim Technologies LTD
AI Copilot
Copilot gives you straightforward answers to real configuration questions.

Finance Module
All-in-one financial management: monitor cash flow, keep accurate records, and gain a better view of your financial health.

Onboarding
Make sure your customers are who they say they are, without forcing them to jump through unnecessary hoops.

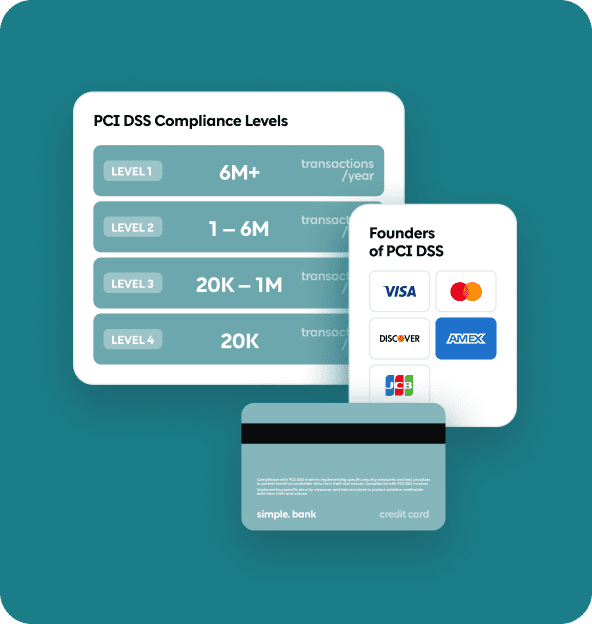
PCI DSS certification
No more hair-tearing. We'll pinpoint your needs, make a plan, and help you become (and stay) compliant.

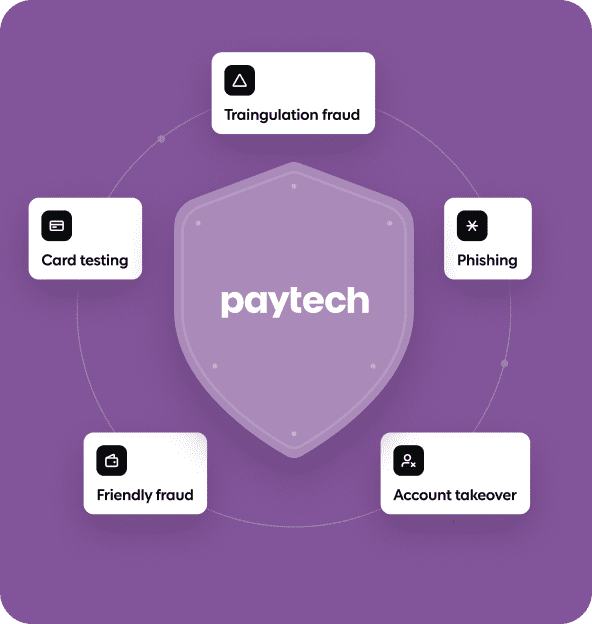
Fraud Prevention
No matter how crafty bad actors get, our sophisticated anti-fraud technology will keep your business three steps ahead.

Development & Support
Got brilliant ideas but lack the know-how to make them happen? Our seasoned developers are ready to step in.

Monitoring
Track key metrics, make better-informed decisions, and fix weak spots before they disrupt your operations.
Roman Andriichuk
Director, Exim Technologies LTD
We always adhere to comfortable interaction within our team and want the best talents to be with us.

Last Update: October 26, 2026 at 17:31
1 Introduction
paytech Ltd values your privacy and is committed to protecting your personal information.
This Privacy Policy (‘Policy’) explains how paytech Ltd (‘paytech Ltd’, ‘we’, ‘us’, ‘our’), a Company incorporated under the laws of the Republic of Cyprus with registration number ΗΕ 440168, with its registered office at Archiepiskopou Makariou III, 84, OFFICE 1, 6017, Larnaca, Cyprus, acting as a Data Controller for the activities described in this Policy, collects and processes your personal information, i.e. information collected online and offline, in accordance with the General Data Protection Regulation (2016/679) and the applicable Data Protection Laws of the Republic of Cyprus (the ‘Law’).
We also process Personal Data on behalf of business clients under their instructions and our Data Processing Agreement. Clients may themselves act for merchants or other customers. This includes our white-label software, payment gateway and payment orchestration services, related integrations and support, and NetworkToken and 3DS2 services where selected. Data may include cardholder and payment details, token records and lifecycle events, transaction information, device or browser information, and authentication requests and results. For this processing, the relevant controller’s privacy notice applies. Please direct rights requests to that controller; we assist our clients under the applicable Data Processing Agreement.
This Policy primarily covers our website and our direct interactions with individuals, including prospective clients and representatives of business clients. Where we process Personal Data on behalf of a business client, the applicable client agreement and Data Processing Agreement govern that processing and the Parties’ contractual obligations. This Policy does not amend those agreements. Where we process Personal Data as an independent controller in connection with our Software or Services, we provide the required information through this Policy or a supplementary privacy notice made available to the affected individuals. Nothing in those agreements limits individuals’ rights under applicable data protection law.
2 Definitions
‘Data Controller’ means the person or organisation which determines when, why and how to process Personal Data and implements appropriate technical and organisational measures to comply with the Law;
‘Data Protection Officer’ means the person who is formally appointed with the purpose of ensuring that we are aware of and comply with our data protection responsibilities and obligations according to the Law;
‘Data Subject’ means a living, identified or identifiable natural person about whom we hold Personal Data;
‘Personal data’ means data about the Data Subject who can be identified: (a) from that data; or (b) from that data and other information to which we have or are likely to have access.
‘Processing’ means any operation or set of operations which is performed on Personal Data or on sets of Personal Data, whether or not by automated means, such as collection, recording, organization, structuring, storage, adaption or alteration, retrieval, consultation, use, disclosure by transmission, dissemination, or otherwise making available, alignment or combination, restriction, erasure or destruction;
‘Special Categories of Personal Data’ means the information revealing racial or ethnic origin, political opinions, religious or similar beliefs, trade union membership, physical or mental health conditions, sexual life, sexual orientation, genetic data, or biometric data used to uniquely identify a person.
We do not intentionally collect Special Categories of Personal Data for ordinary website enquiries or business account administration. If such data is necessary for a specific activity, we will explain the purpose and identify both a lawful basis under Article 6 GDPR and an applicable condition under Article 9 GDPR before processing it. For the purposes of this Policy, Personal Data includes Special Categories of Personal Data;
‘the Law’ means the General Data Protection Regulation (2016/679) (GDPR) and the applicable Data Protection Laws of the Republic of Cyprus;
‘Third Party’ means the recipient of your Personal Data as defined below.
3 The Principles of Law
4 The kind of information we collect about the Data Subjects
The purpose of the Processing of the Personal Data of the Data Subjects is largely based on each of the Services that the Data Subject has requested. In general, the Personal Data is processed, within the scope of the business relationship with the Data Subjects.
We receive Personal Data directly from you, through your use of our website, and from the business client or organisation you represent when it provides your business contact details. Where information is required to respond to your enquiry, perform a contract or comply with a legal obligation, failure to provide it may prevent us from responding or providing the relevant Service. Optional information is not required.
Further information about cookies and similar technologies, including how to manage your preferences, is available in our Cookies Policy.
5 On what legal basis do we process the Personal Data
We collect, store, use and disclose Personal Data for the following purposes and on the following legal bases:
We do not make decisions based solely on automated processing that produce legal or similarly significant effects on you in the activities for which we act as a Data Controller under this Policy.
6 Who Receives your Personal Data
Your Personal Data may be accessed by the following persons where necessary for the purposes set out above:
7 Transferring your Personal Data outside European Union (‘EU’) and European Economic Area (‘EEA’)
Where providing our website or Services involves transferring Personal Data outside the EEA, including access by a recipient in another country, we ensure that the transfer meets the requirements of the Law. You may contact us using the details below for information about the applicable transfer safeguards and to obtain a copy.
8 When can Personal Data be transferred outside of the EU and the EEA
9 Retention of Personal Data
We will retain the Personal Data of the Data Subjects for as long as it is necessary to fulfil the purpose for which it was collected (including for the purposes of satisfying any legal, accounting or reporting requirements). We will cease to retain Personal Data of the Data Subjects or remove the means by which the Personal Data can be associated with them (i.e. anonymize the Personal Data) as soon as this retention no longer serves the purposes for which the Personal Data were collected (except where retention is required by applicable laws). Retention is determined by the duration of the business relationship, the time needed to resolve an enquiry or support request, applicable statutory retention periods and relevant limitation periods for legal claims. Security logs are retained for the period needed to investigate and prevent misuse. Cookie durations are described in our Cookies Policy. Anonymisation means that an individual is no longer identifiable by means reasonably likely to be used. Removing names or replacing card details with tokens does not, by itself, anonymise data.
10 Protection of Personal Data
To safeguard all Personal Data from unauthorized access, collection, use, damage, loss disclosure, copying or similar risks, we have introduced appropriate administrative, physical and technical measures including appropriate access controls and encryption where warranted by the risks. We also allow access to Personal Data only to those employees who need to know such data and they will only process Personal Data on our instructions. However, no method of transmission over the internet or method of electronic storage is completely secure. While security cannot be guaranteed, we try to protect the security of the Data Subject’s Personal Data and we constantly review and enhance our information security measures.
11 The rights of the Data Subjects in relation to their Personal Data
These rights apply subject to the conditions and exceptions in the Law. You may also withdraw consent as described above.
Kypranoros 15, 1061 Nicosia, Cyprus
Postal address: P.O. Box 23378, 1682 Nicosia, Cyprus
Tel: +357 22818456
Fax: +357 22304565
Email: [email protected]
Website: Office of the Commissioner for Personal Data Protection
12 How can you exercise your rights in relation to your Personal Data
If you wish to exercise any of your rights, you may contact our Data Protection Officer in writing or via email at the contact details provided below:
Name: PANAYIOTIS Z. TOULOURAS LLC
Address: Rafail Santi 58, NEFELI COURT 11, Ground Floor, 6052, Larnaca, Cyprus
Email: [email protected]
Where we have reasonable doubts about your identity, we may request additional information necessary to confirm it.
We will respond without undue delay and within one month of receiving your request. Where necessary because of its complexity or the number of requests, we may extend this by up to two further months and will explain the extension within the first month. Requests are normally free of charge. Any refusal or fee will be limited to circumstances permitted by law and accompanied by an explanation and information about your remedies.
13 Effect of Policy and Changes to Policy
We keep this Policy under review and may update it from time to time by publishing a revised version and updating the date above. We will provide additional notice where required by law, including before processing your Personal Data for a new purpose. Please review this Policy periodically.


